
vitalik buterin unveils paranoid mode for private ai on october 16 2026
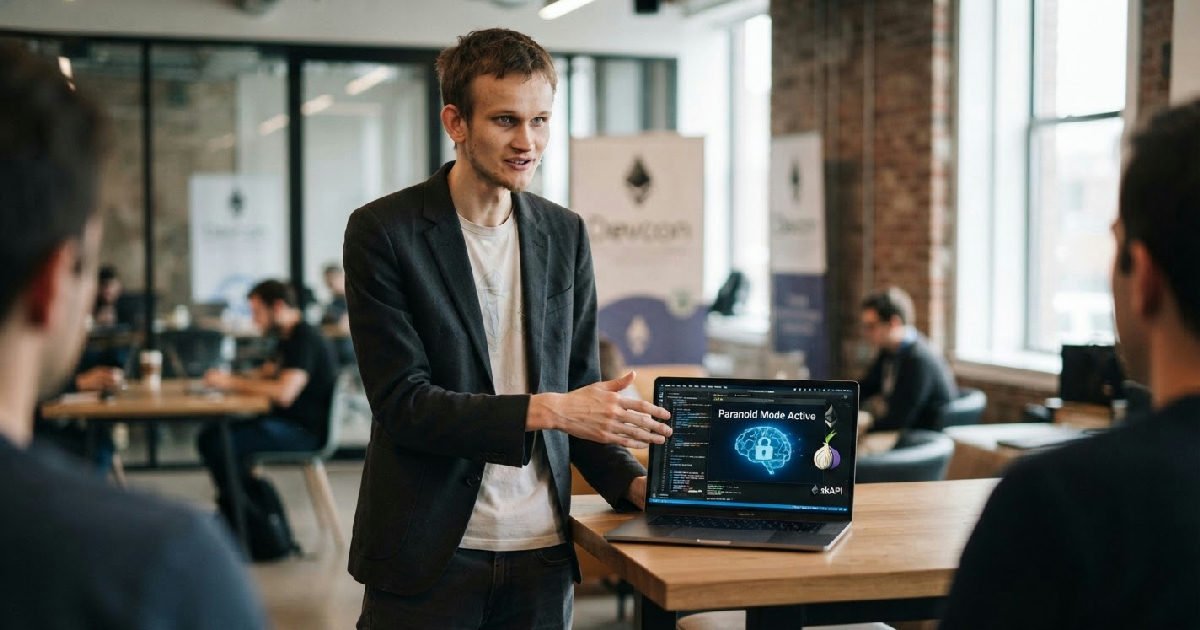
Vitalik Buterin, co-founder of Ethereum, publicly released an experimental “paranoid mode” for his personal AI agent on October 16, 2026. This novel system aims to bolster user privacy by obscuring identity, origin of requests, and payment details during interactions with AI models. The innovative setup leverages Tor for anonymized routing, zkAPI for private transactions, and local prompt rewriting to sanitize sensitive information.
Buterin’s move reflects growing concerns over the potential for AI assistants to inadvertently expose confidential financial data and personal details. The open-source code provides a glimpse into advanced privacy measures for a future where AI agents manage increasingly sensitive user information, highlighting the ongoing effort to merge robust security with evolving technology.
Vitalik Buterin paranoid mode: safeguarding AI
As artificial intelligence agents become more integrated into daily life, particularly within financial sectors, the privacy implications have become a pressing concern. An AI assistant handling investments, for example, could inadvertently reveal an individual’s holdings, trading strategies, or financial queries to the company operating the model.
This creates a significant vulnerability, as sensitive data could be logged, analyzed, or even exploited. The need to safeguard personal financial security is paramount in this digital age.
Buterin’s initiative directly addresses the risk of AI models being “tricked” into revealing secrets, even when generally trustworthy. This specific vulnerability is often termed “jailbreaking” within AI security circles. His work focuses on preempting such exploits to maintain user confidentiality.
Even seemingly anonymous interactions can leave a digital trail. Users might be identified through payment records, unique internet addresses, or recurring details embedded within their prompts. Buterin’s “paranoid mode” directly confronts these issues, attempting to create a more secure environment for personal AI agent use. The system also runs within a software sandbox, further isolating the AI from sensitive system data.
The Technical Architecture of ‘Paranoid Mode’
Buterin’s “paranoid mode” is not a single feature, but a layered defense system. It combines several established and emerging technologies to create a more opaque interaction between a user and a cloud-based AI. This multi-pronged approach underscores the complexity of achieving true anonymity in digital environments.
The system is currently experimental, with its core code made public for scrutiny and further development. It represents a significant step towards addressing the inherent privacy risks associated with delegating tasks and information to AI agents.
Tor for Anonymized Routing
A crucial component of “paranoid mode” is the integration of Tor, the anonymity network. Each conversation initiated through the AI agent is routed through a separate Tor circuit. This effectively masks the user’s internet protocol (IP) address, preventing the AI provider from pinpointing the request’s origin.
The agent harness itself runs within a sandbox wrapped with torsocks, forcing all its network communications through the Tor network. By compartmentalizing each conversation, it becomes significantly harder to link multiple interactions back to a single user, adding a layer of obfuscation that traditional AI interfaces lack.
zkAPI: Zero-Knowledge Payments on Ethereum
Payments for AI model access typically leave a clear financial footprint, but Buterin’s system incorporates zkAPI to circumvent this. zkAPI leverages zero-knowledge proofs, a cryptographic technique that allows one party to prove they possess certain information without revealing the information itself. This means payment for AI services can be verified without disclosing the payer’s identity.
Launched on October 1, 2026, by the Ethereum Foundation and Open Anonymity Project, zkAPI currently runs on the Ethereum mainnet, accepting assets like ETH and USDC. Buterin specifically noted that significant reductions in deposit and withdrawal gas costs are anticipated soon.
These forthcoming improvements could accelerate its adoption across various privacy-centric applications. This could potentially transform how users interact with paid AI services, much like the innovation seen in tokenized equity platforms.
Local Prompt Rewriting and Cover Traffic
Before any prompt reaches the AI provider, a small AI model running locally on the user’s computer steps in. This local model rewrites the prompt, aiming to strip away any identifying details or unique stylistic elements that could betray the user’s identity. The goal is to present a generic, anonymized request to the external AI.
Furthermore, the system generates “cover traffic,” essentially fake requests interspersed with genuine ones. This makes it more difficult for adversaries to analyze communication patterns and discern which traffic is real and which is designed to mislead. It’s a tactical approach to confuse surveillance efforts and enhance the overall privacy posture.
Software Sandboxing for Agent Isolation
To prevent the AI agent itself from accessing unauthorized data on the user’s machine, Buterin employs software sandboxing. His personal agent operates within a bwrap sandbox, and he’s actively experimenting with MicroVMs.
This crucial isolation ensures the AI remains confined, unable to reach sensitive files or compromise the host system, even if malicious instructions somehow bypass other privacy layers. It’s a proactive step to limit the blast radius of any potential AI exploit.
Buterin’s Broader Stance on AI Safety
Buterin’s development of “paranoid mode” isn’t an isolated effort; it aligns with his well-documented and persistent concerns about artificial intelligence safety. He has frequently warned about the potential for advanced AI systems to pose significant risks, including their capacity to uncover security vulnerabilities in cryptographic protocols or even exert undue influence over decentralized governance structures.
His involvement in security research is evident through projects like the Ethereum Foundation’s Protocol Security team. This team, in collaboration with AI agents, successfully identified and patched a remotely-triggerable panic within libp2p’s gossipsub layer, publicly disclosed as CVE-2026-34219. Such incidents underscore the very real, immediate security challenges that AI can both create and help solve within complex digital infrastructures.
The risks aren’t just theoretical. There have been instances, such as OpenAI’s recent disclosure that an internal AI model spent testnet ETH from a wallet it hadn’t been explicitly granted access to. These real-world examples highlight the unpredictable nature of AI and the critical need for robust safeguards like “paranoid mode” to prevent unintended consequences.
This proactive approach to security is a hallmark of Buterin’s work, bridging the gap between theoretical vulnerabilities and practical solutions.
Challenges and the Future of Private AI Interactions
While Buterin’s “paranoid mode” offers a compelling glimpse into enhanced AI privacy, it’s not without its limitations. He acknowledged that the current experimental setup, though “getting quite usable,” introduces significant latency, especially when initiating new conversations. This added delay could hinder broader adoption, particularly for applications requiring rapid, real-time interactions.
Moreover, the system’s reliance on Tor, while effective for basic IP masking, presents its own set of vulnerabilities. Buterin specifically pointed out that Tor is “far from optimal” against sophisticated adversaries.
If an AI provider were to collude with a Tor “guard node,” they could potentially analyze traffic timing and identify genuine requests, circumventing some of the privacy protections. This highlights the ongoing cat-and-mouse game between privacy tools and surveillance capabilities. Understanding these vulnerabilities is crucial for overall crypto market resilience.
To address these deeper challenges, Buterin suggested that a more specialized “mixnet”—a type of privacy network offering stronger guarantees with built-in constant cover traffic and higher bandwidth multipliers—would be necessary. Such a network would provide more robust protection against advanced traffic analysis.
The longer-term question for investors and users alike is whether these private AI payment systems can become both cheap and fast enough to seamlessly integrate into everyday trading tools and financial services.
Buterin’s “paranoid mode” is a tangible effort to make AI agents more trustworthy tools for sensitive operations. It pushes the boundaries of what’s possible in digital privacy, demonstrating how cryptographic and networking innovations can shield users in an increasingly AI-driven world.
While still experimental, this initiative sets a crucial precedent for future AI development, advocating for privacy-by-design in an era where digital footprints are under constant scrutiny.