
crypto sector reports 1.18 billion dollar losses q3 2026
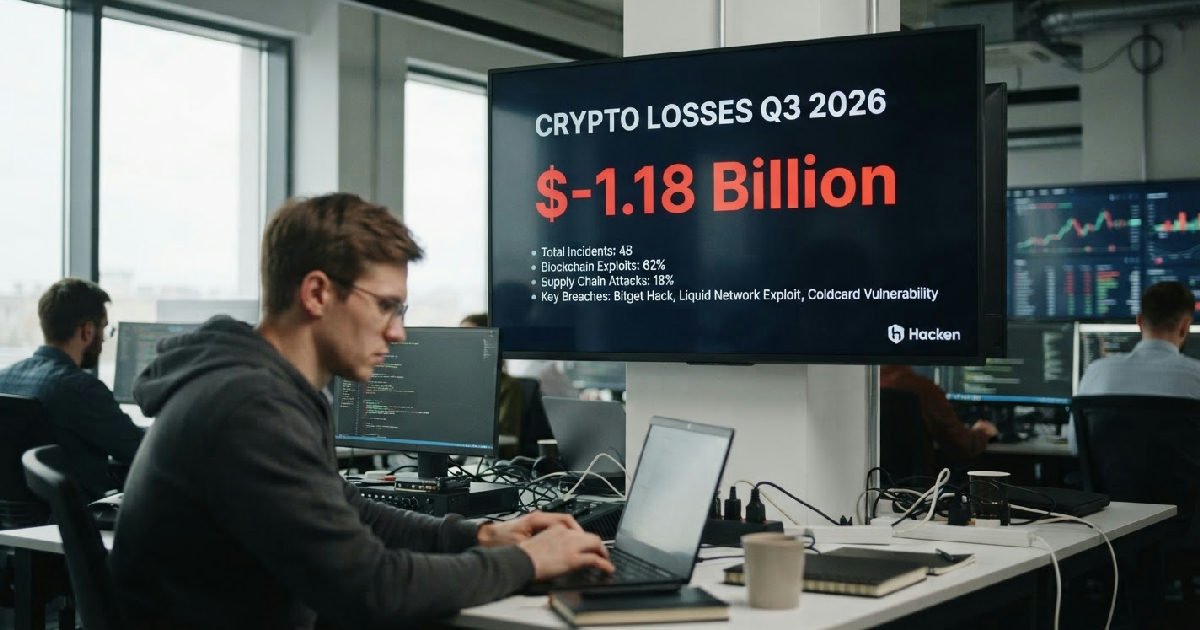
The cryptocurrency sector endured a stark increase in financial losses during the third quarter of 2026, with security breaches costing the industry an estimated $1.18 billion. This substantial figure, detailed in a new report from blockchain security firm Hacken released on October 15, 2026, represents a 55% surge in damages compared to the previous quarter.
Attackers leveraged vulnerabilities across 107 separate incidents, marking a worrying trend for digital asset security.
Q3 2026 sees crypto losses hit $1.18 billion mark
Crucially, the Hacken report highlights a significant shift in attacker tactics. A staggering 77% of these losses, totaling approximately $906.8 million, did not stem from direct exploits of smart contract code but rather from compromised suppliers, delayed security patches, and un-audited infrastructure components. This indicates a more sophisticated and systemic target for malicious actors within the crypto ecosystem.
The third quarter of 2026 proved to be one of the most perilous periods for crypto security in recent memory. Total losses soared to $1.18 billion, a sharp escalation from the $763.97 million recorded in Q2 2026. This increase occurred despite a market that often sees reduced trading volumes and, at times, complacency regarding security measures.
Hacken’s analysis meticulously documented 107 security incidents throughout July, August, and September. Of those 107 breaches, 63 were associated with losses exceeding $250,000, underscoring the severity of the attacks. It also stands as the most damaging period for the industry since Q1 2025, which saw $1.6 billion in losses, largely due to the Bybit breach.
The median loss per individual hack stood at $670,000, illustrating that while a few major events captured headlines, a consistent drumbeat of smaller, yet still significant, breaches contributed to the overall toll. In fact, 98 of the 107 recorded security incidents produced losses below $10 million each, indicating widespread vulnerabilities across various platforms.
The broader market also considers how AI in crypto trading impacts sentiment and security.
Shifting attack vectors: The rise of supply chain exploits
The most striking finding from Hacken’s report is the fundamental shift in how attackers are compromising digital asset platforms. A dominant 77% of the total Q3 2026 crypto losses, amounting to $906.8 million, originated from vulnerabilities beyond direct smart contract code. This marks a significant evolution from previous quarters where smart contract flaws often took center stage.
Instead, hackers successfully exploited weaknesses tied to compromised third-party suppliers, critical security patches that were either delayed or never deployed, and infrastructure components that operated outside standard security audits. This trend highlights a growing reliance on external systems and processes within the crypto ecosystem, creating new attack surfaces that are often less scrutinized.
These broader security gaps indicate that the industry’s focus must expand beyond just code integrity. Attackers are increasingly targeting the operational periphery of crypto projects, exploiting interconnected systems and human processes. It’s a clear signal that the ecosystem’s weakest links are now often found in its wider supply chain and third-party integrations.
Case studies in systemic vulnerability
Several high-profile incidents during Q3 2026 starkly illustrate these systemic vulnerabilities. Cryptocurrency exchange Bitget suffered the largest single loss, approximately $387.5 million, when hackers exploited a zero-day flaw within a third-party security software package to generate fraudulent withdrawal requests. This type of sophisticated attack underscores the danger of relying on external software without robust internal verification.
Similarly, the Cosmos EVM chain lost an estimated $5.7 million due to its failure to implement a crucial security update within 96 days of its release. This created a critical window for underflow exploits against chains that had not yet patched the known vulnerability.
Even hardware wallets proved susceptible: Coldcard experienced $115 million in losses after a build check flaw introduced a weakness into its hardware wallet seed generation process, an error that should have been identified during routine software configuration procedures.
Concentrated damage from high-impact incidents
While the overall number of incidents was high, a significant portion of the financial damage in Q3 2026 stemmed from a handful of exceptionally large breaches. Just four major incidents accounted for approximately 80% of the quarter’s total reported losses, revealing a concentration of risk in specific, high-value targets.
This pattern highlights how a few critical failures can disproportionately impact the industry’s security landscape, even as predictions for a Ripple DeFi breakthrough remain optimistic.
Beyond the Bitget incident, the Liquid Network experienced a $320 million exploit, making it one of the quarter’s most substantial thefts. Another significant event was the Tectonic exploit, which led to $120 million in losses. These events, combined with the aforementioned Coldcard vulnerability, underscore how compromised infrastructure, rather than direct smart contract bugs, are now driving the most damaging attacks.
The magnitude of these individual incidents reflects a dangerous evolution in attacker capabilities. It suggests that while the industry has made strides in securing smart contracts, vulnerabilities in broader system architecture, third-party dependencies, and operational security remain lucrative targets for sophisticated threat actors. This trend complicates the overall defense strategy for digital asset firms.
Industry grapples with response and recovery efforts
Despite the staggering losses, the third quarter also saw notable efforts in fund recovery and mitigation. Approximately $387 million, or about 33% of the gross losses, was either returned to victims or successfully reversed. These recoveries often involved swift action from affected platforms and collaboration with white-hat hackers and other security entities.
For instance, self-proclaimed white hats were instrumental in recovering about 85% of the stolen funds from the Liquid Network hack, returning $272 million. The Tectonic incident saw Cronos validators execute a blockchain rollback of 114 minutes, successfully reversing approximately $111.2 million of the $120.4 million in affected borrowing.
Furthermore, stablecoin issuers Circle and Tether froze about $340,000 linked to the Bitget theft, limiting the attackers’ ability to cash out. Operators also covered an additional $410 million of user losses directly from their own funds, demonstrating a commitment to customer protection, though approximately $384 million remained unrecovered for users.
The path forward: Enhanced audits and continuous monitoring
In light of these findings, Hacken has urged the cryptocurrency industry to significantly expand its security audit scope. The firm recommends including privileged components such as oracles, bridgers, and custody systems, which are often overlooked in traditional smart contract audits. This broader approach is crucial for addressing the new vectors of attack that dominated Q3 2026.
The report also stresses the necessity of timely patching and continuous monitoring across all connected infrastructure. Attackers are often exploiting known weaknesses that firms fail to address quickly enough, suggesting that the problem isn’t always identification but execution. Continuous monitoring could help teams track new threats, fix urgent weaknesses, and confirm that updates reach all affected systems.
Moreover, Hacken highlighted that audit badges can be misleading. Many audits cover only selected smart contracts, leaving crucial systems unexamined, yet investors often assume an audit applies to an entire platform. This discrepancy underscores the need for greater transparency and more comprehensive security reviews across the entire digital asset ecosystem.
The industry must move towards a more holistic security posture, where supply chain risks and operational processes are as rigorously vetted as smart contract code.
The increasing complexity of crypto security threats demands proactive measures. With crypto market liquidation events becoming more frequent due to various factors, ensuring robust security is paramount to maintaining investor confidence and the overall stability of the digital asset space. Firms must prioritize investment in security infrastructure and personnel to keep pace with evolving threats.
This evolving threat landscape signifies a critical juncture for the crypto industry. The shift from direct smart contract exploits to broader infrastructure and supply chain vulnerabilities calls for a re-evaluation of security paradigms.
For platforms hoping to avoid the kind of losses seen this past quarter, comprehensive security from end-to-end, including all third-party integrations and internal processes, will be non-negotiable. This proactive stance is essential to protect assets and ensure user trust as the market continues its rapid evolution.